-
n8n Warns of CVSS 10.0 RCE Vulnerability Affecting Self-Hosted and Cloud Versions
Open-source workflow automation platform n8n has warned of a maximum-severity security flaw that, if successfully exploited,…
-
Critical n8n Vulnerability (CVSS 10.0) Allows Unauthenticated Attackers to Take Full Control
Cybersecurity researchers have disclosed details of yet another maximum-severity security flaw in n8n, a popular workflow…
-
Black Cat Behind SEO Poisoning Malware Campaign Targeting Popular Software Searches
A cybercrime gang known as Black Cat has been attributed to a search engine optimization (SEO)…
-
Webinar: Learn How AI-Powered Zero Trust Detects Attacks with No Files or Indicators
Security teams are still catching malware. The problem is what they’re not catching. More attacks today…
-
CISA Flags Microsoft Office and HPE OneView Bugs as Actively Exploited
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added two security flaws impacting Microsoft…
-
OpenAI Launches ChatGPT Health with Isolated, Encrypted Health Data Controls
Artificial intelligence (AI) company OpenAI on Wednesday announced the launch of ChatGPT Health, a dedicated space…
-
Coolify Discloses 11 Critical Flaws Enabling Full Server Compromise on Self-Hosted Instances
Cybersecurity researchers have disclosed details of multiple critical-severity security flaws affecting Coolify, an open-source, self-hosting platform,…
-
Researchers Uncover NodeCordRAT Hidden in npm Bitcoin-Themed Packages
Cybersecurity researchers have discovered three malicious npm packages that are designed to deliver a previously undocumented…
-
Cisco Patches ISE Security Vulnerability After Public PoC Exploit Release
Cisco has released updates to address a medium-severity security flaw in Identity Services Engine (ISE) and…
-
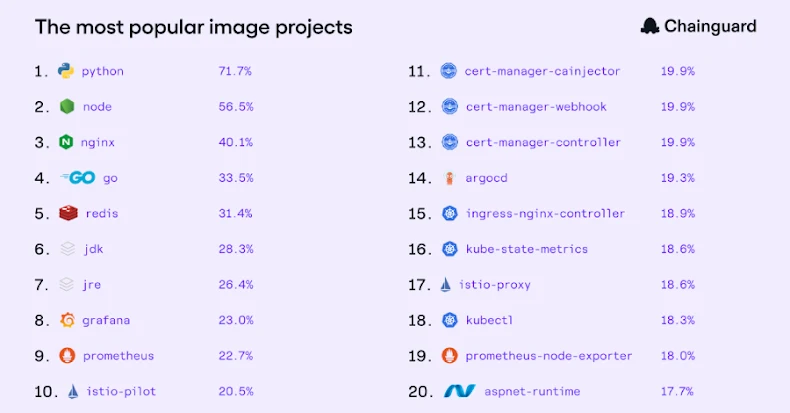
The State of Trusted Open Source
Chainguard, the trusted source for open source, has a unique view into how modern organizations actually…
Latest Posts
- Drones to Diplomas: Russia’s University Linked to $25M Essay Mill
- The Kimwolf Botnet is Stalking Your Local Network
- Who Benefited from the Aisuru and Kimwolf Botnets?
- Windows 11 PCs may fail to shut down after January update: Microsoft confirms
- Cisco Patches AsyncOS Zero-Day Exploited Since November 2025