-
New n8n Vulnerability (9.9 CVSS) Lets Authenticated Users Execute System Commands
A new critical security vulnerability has been disclosed in n8n, an open-source workflow automation platform, that…
-
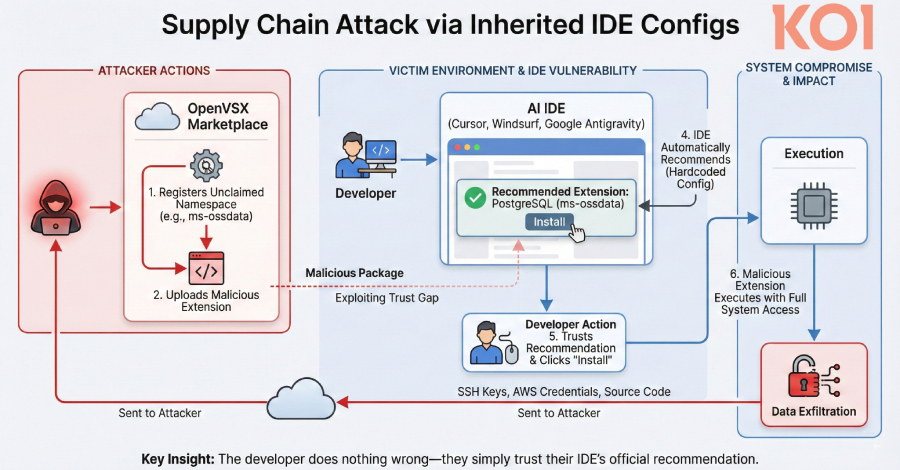
VS Code Forks Recommend Missing Extensions, Creating Supply Chain Risk in Open VSX
Popular artificial intelligence (AI)-powered Microsoft Visual Studio Code (VS Code) forks such as Cursor, Windsurf, Google…
-
What is Identity Dark Matter?
The Invisible Half of the Identity Universe Identity used to live in one place – an…
-
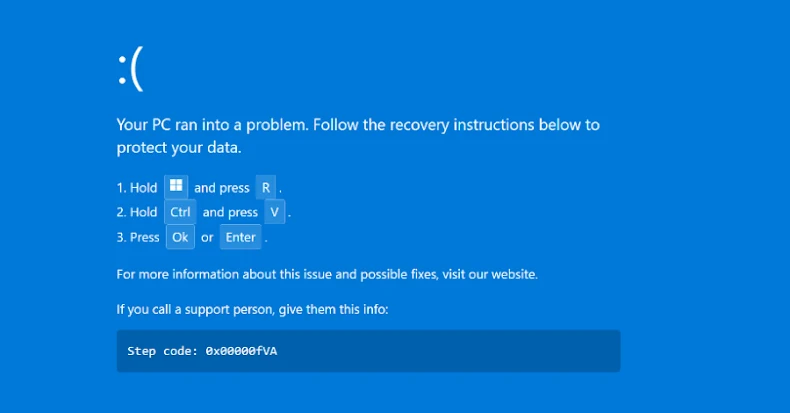
Fake Booking Emails Redirect Hotel Staff to Fake BSoD Pages Delivering DCRat
Cybersecurity researchers have disclosed details of a new campaign dubbed PHALT#BLYX that has leveraged ClickFix-style lures…
-
Unpatched Firmware Flaw Exposes TOTOLINK EX200 to Full Remote Device Takeover
The CERT Coordination Center (CERT/CC) has disclosed details of an unpatched security flaw impacting TOTOLINK EX200…
-
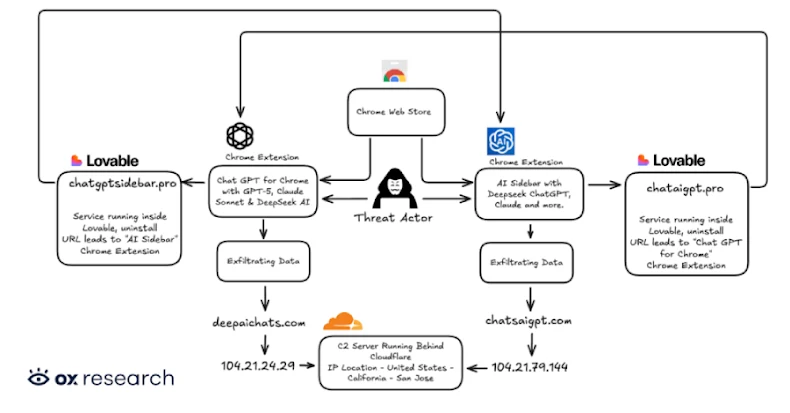
Two Chrome Extensions Caught Stealing ChatGPT and DeepSeek Chats from 900,000 Users
Cybersecurity researchers have discovered two new malicious extensions on the Chrome Web Store that are designed…
-
Ongoing Attacks Exploiting Critical RCE Vulnerability in Legacy D-Link DSL Routers
A newly discovered critical security flaw in legacy D-Link DSL gateway routers has come under active…
-
Microsoft Warns Misconfigured Email Routing Can Enable Internal Domain Phishing
Threat actors engaging in phishing attacks are exploiting routing scenarios and misconfigured spoof protections to impersonate…
-
Veeam Patches Critical RCE Vulnerability with CVSS 9.0 in Backup & Replication
Veeam has released security updates to address multiple flaws in its Backup & Replication software, including…
-
The Future of Cybersecurity Includes Non-Human Employees
Non-human employees are becoming the future of cybersecurity, and enterprises need to prepare accordingly. As organizations…
Latest Posts
- Drones to Diplomas: Russia’s University Linked to $25M Essay Mill
- The Kimwolf Botnet is Stalking Your Local Network
- Who Benefited from the Aisuru and Kimwolf Botnets?
- Windows 11 PCs may fail to shut down after January update: Microsoft confirms
- Cisco Patches AsyncOS Zero-Day Exploited Since November 2025