-
Law Firm Data Breach Impacts Goldman Sachs and JPMorgan Chase
A data breach at a law firm has exposed sensitive information belonging to financial giants Goldman…
-
GoBruteForcer Botnet Targeting Crypto & Blockchain Projects
A large-scale botnet named GoBruteForcer is actively targeting cryptocurrency and blockchain projects, posing significant security risks.
-
Microsoft Patches Exploited Windows Zero-Day and Other Vulnerabilities
Microsoft addresses an actively exploited Windows zero-day and 111 other vulnerabilities in its latest security update.
-
CISA Flags Microsoft Office and HPE OneView Bugs as Actively Exploited
CISA adds Microsoft Office and HPE OneView vulnerabilities (CVE-2009-0556, CVE-2025-37164) to KEV, urging agencies to patch…
-
CISA Warns of Active Exploitation of Gogs Vulnerability
CISA warns of active exploitation of a high-severity flaw in Gogs that can lead to remote…
-
New Malware Campaign Delivers Remcos RAT via Windows Attack
SHADOW#REACTOR campaign uses VBS, PowerShell, and MSBuild to deploy Remcos RAT with persistent remote access.
-
ServiceNow Patches Critical AI Platform Flaw Allowing Unauthenticated User Impersonation
ServiceNow fixed CVE-2025-12420, a critical flaw that let unauthenticated attackers impersonate users on its AI Platform.
-
What Should We Learn From How Attackers Leveraged AI in 2025?
Attackers in 2025 scale proven tactics like supply chain attacks and phishing using automation and AI.
-
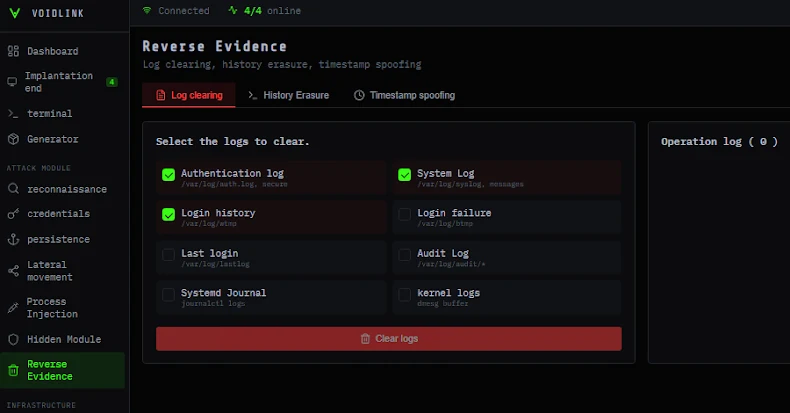
New Advanced Linux VoidLink Malware Targets Cloud and Container Environments
Check Point reveals VoidLink, a China-linked Linux malware built for cloud environments with modular plugins, rootkit…
-
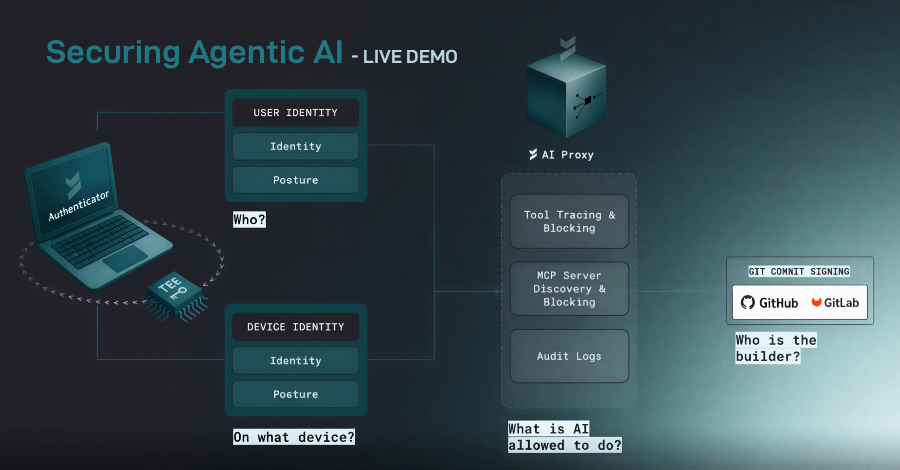
[Webinar] Securing Agentic AI: MCPs, Tool Access, and API Key Sprawl
Learn how to secure AI agents and prevent code execution attacks. Discover MCPs, API key sprawl,…
Latest Posts
- Drones to Diplomas: Russia’s University Linked to $25M Essay Mill
- The Kimwolf Botnet is Stalking Your Local Network
- Who Benefited from the Aisuru and Kimwolf Botnets?
- Windows 11 PCs may fail to shut down after January update: Microsoft confirms
- Cisco Patches AsyncOS Zero-Day Exploited Since November 2025